Banking tokens, domain logins, server credentials, recovery codes: in most organisations they sit with one person, one password manager admin, or one spreadsheet. When that person is on holiday, walks out, or is suddenly gone, the work stops.
In Inheriti® Business the secret belongs to the organisation, not to a person. A plan is scoped to teams, and members reach it through their team, so a second and a third person can always get there. No single person, and no single component, is a complete path to the data.
Day-to-day access to the credentials and secrets a team works with. A member requests access, the plan’s moderators approve, and the data is revealed.
For the day the plan’s creator cannot answer. A Dead Man Switch arms only when someone requests access: the creator is asked to respond, and one response stops it. It sits on top of authentication and moderation, never in their place.
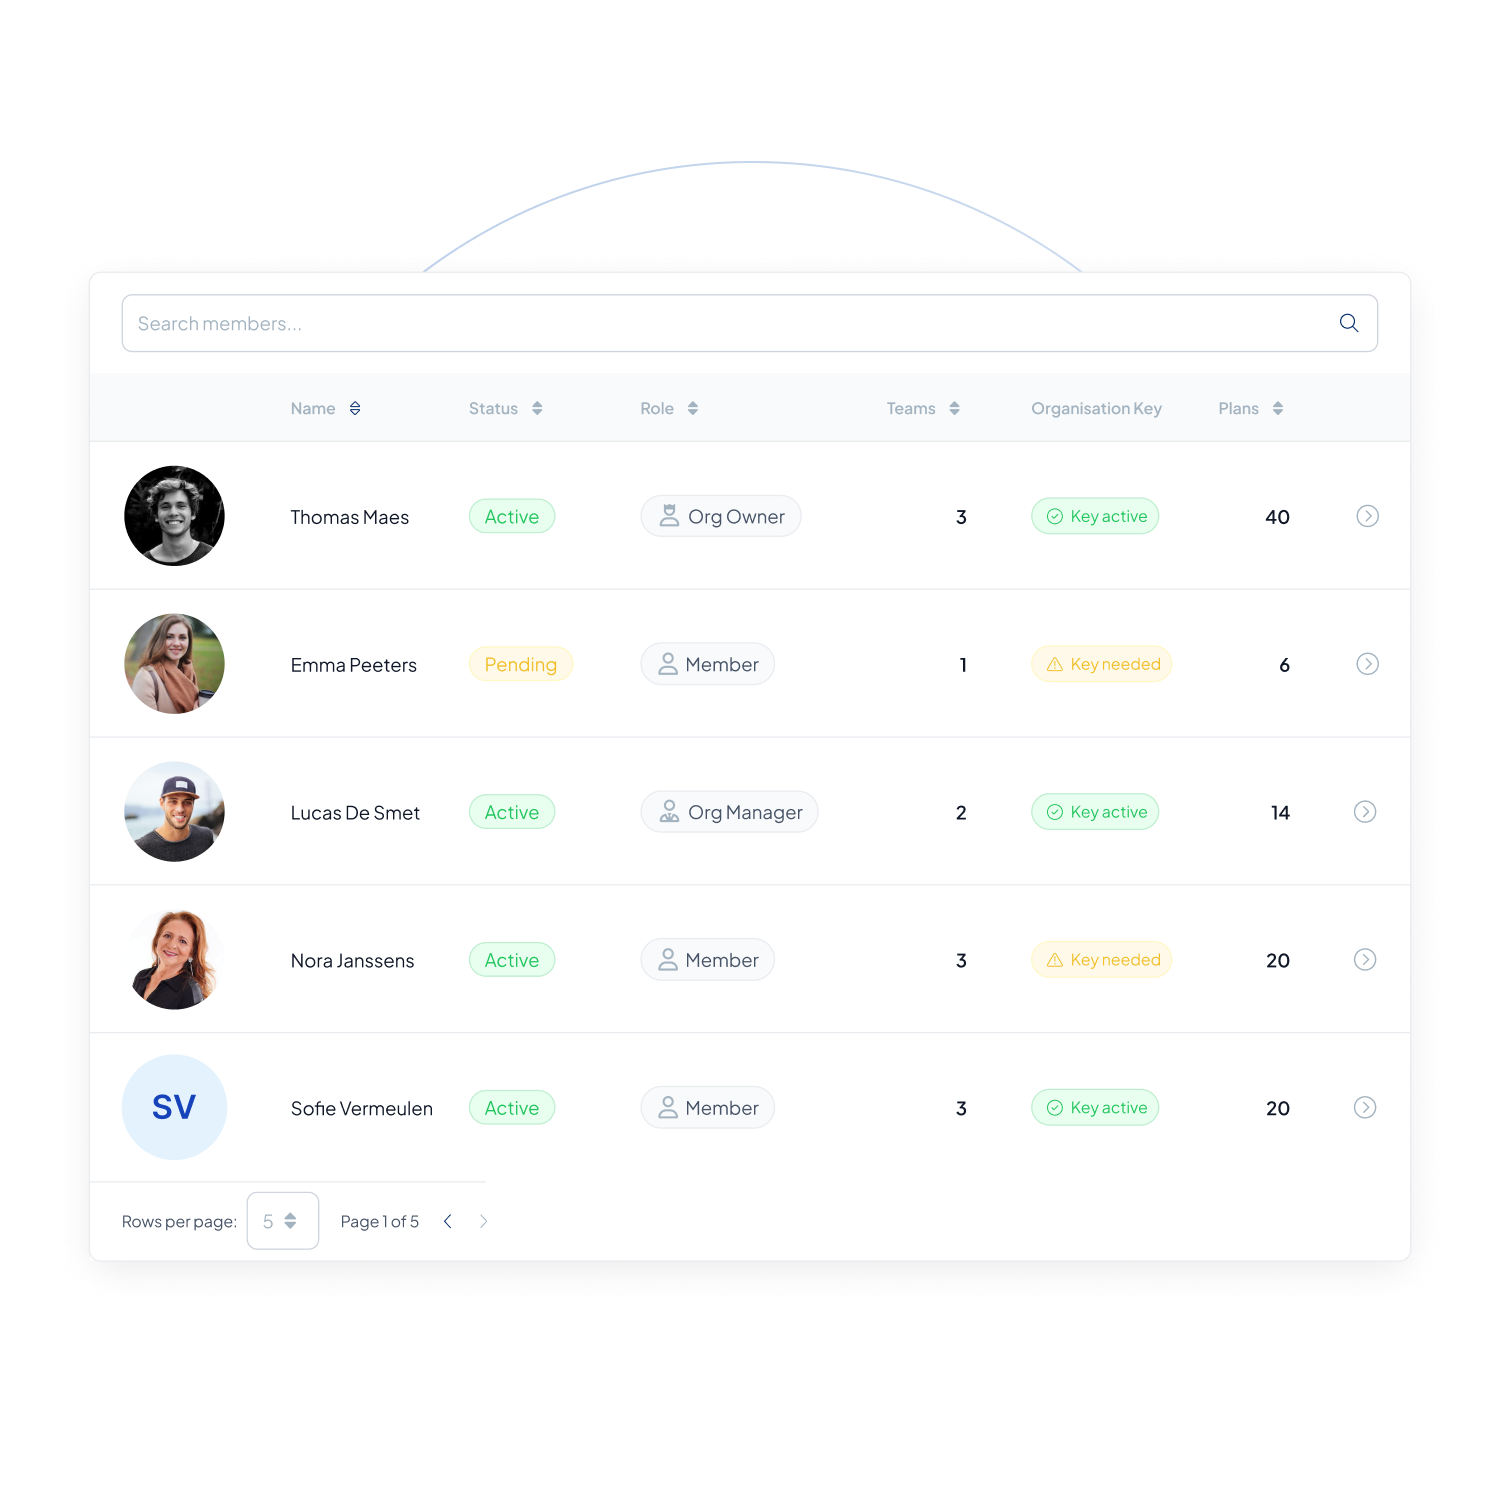
Offboarding closes a mailbox and leaves the shared passwords untouched, still in someone’s head or in an export they made last year. You cannot even list what needs changing.
Your organisation is built from members and teams, and teams hold plan access. Remove a member, or move them out of a team, and their share access records are marked invalid. Nothing has to be re-encrypted: every request is checked against your organisation as it stands at that moment, so the person must still be active and still authorised by their team and role.
Whatever their device still holds is inert. Rotate the plan or the secret and the old share ciphertext is purged as well.
An auditor, a client or an incident asks the question, and the honest answer is usually a shrug. A technical gap turns into a personal one.
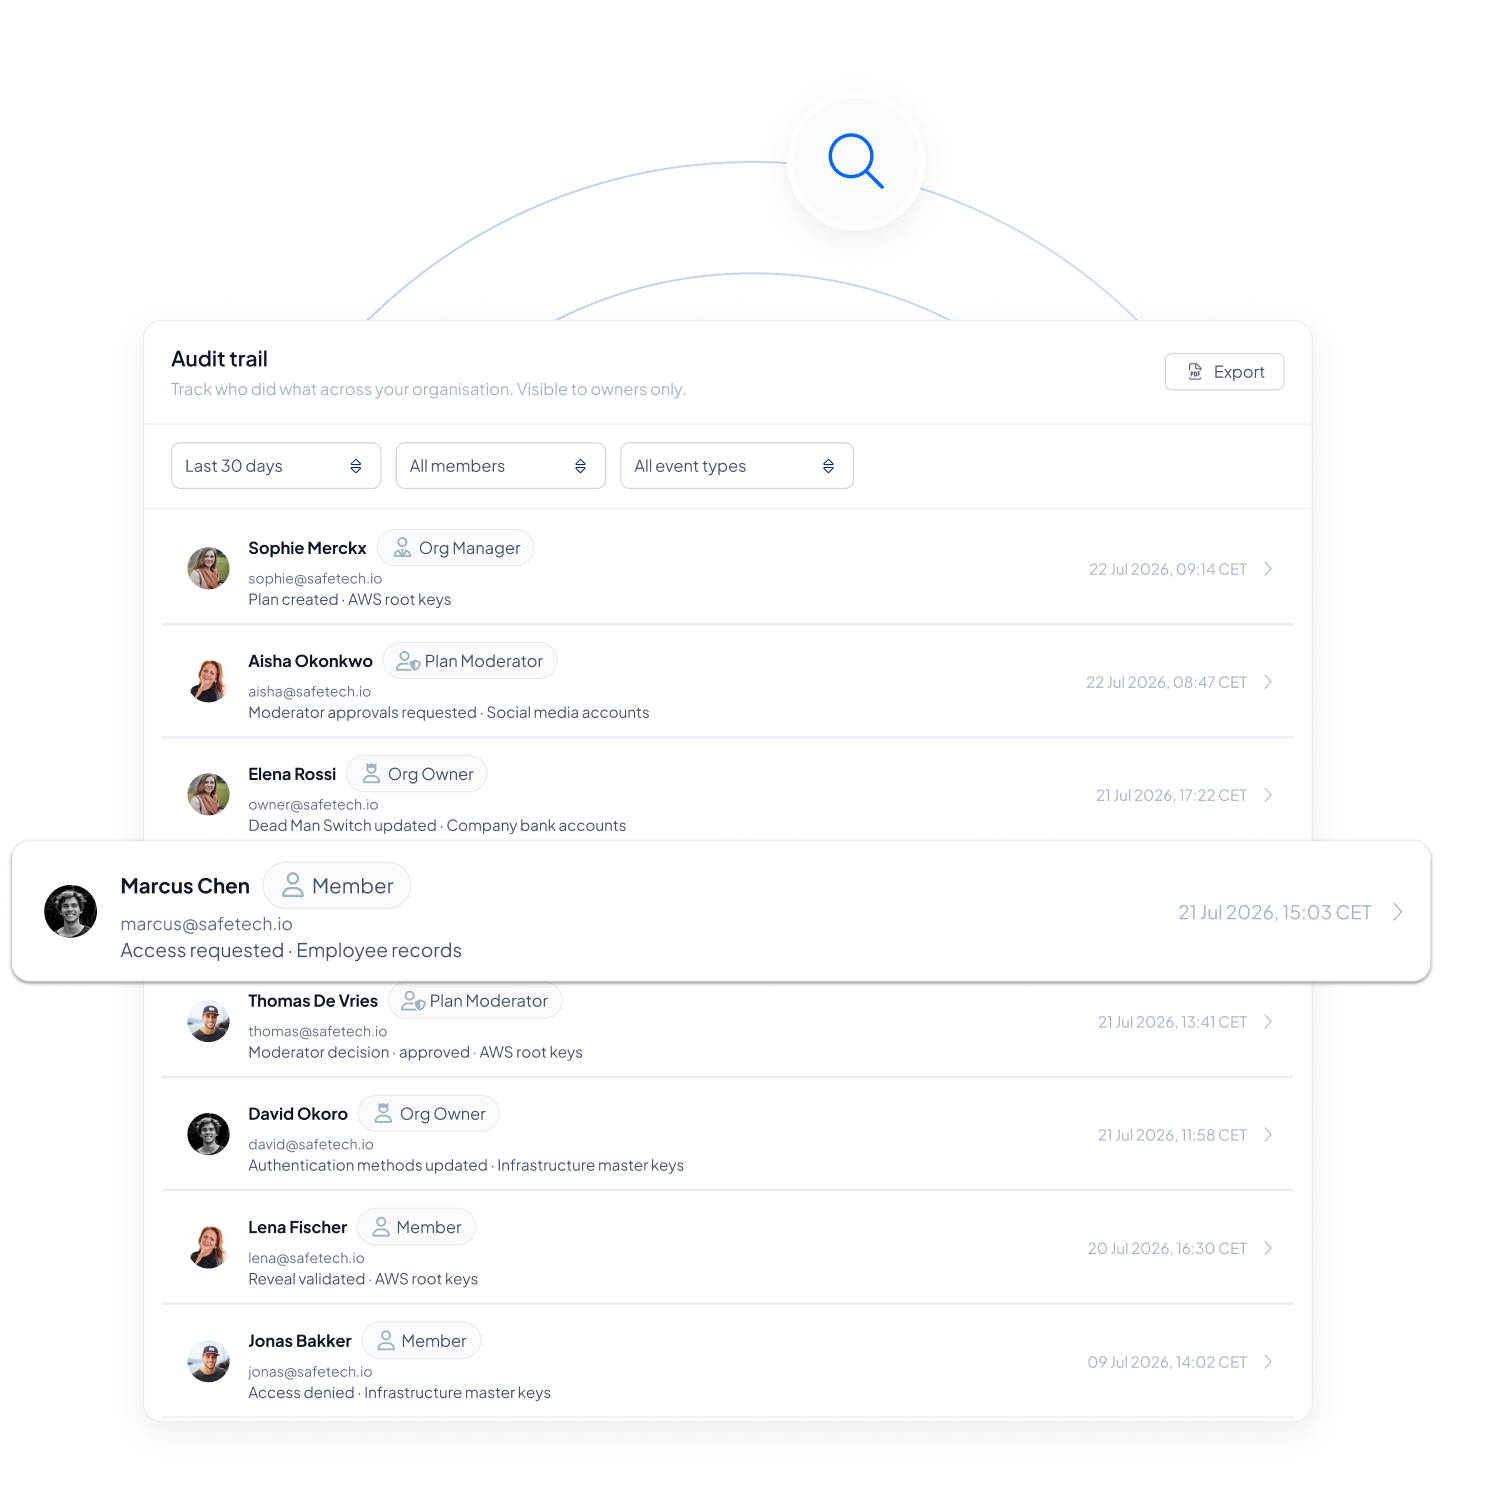
Every access request, approval, denial and reveal lands in your organisation’s audit trail, next to authentication, moderation, data asset, membership, storage and subscription events. Export the full trail as a report, or a scoped log for a single member, team, plan or storage layer.
Each report closes with an integrity page: a SHA-256 hash of the document, its reference and its scope. The plan register inside it describes configuration only, never protected content.
The spreadsheet, the chat message, the private password manager, the note in a drawer: every copy of a secret is a leak waiting for a reason, and you cannot take back what you already handed out.
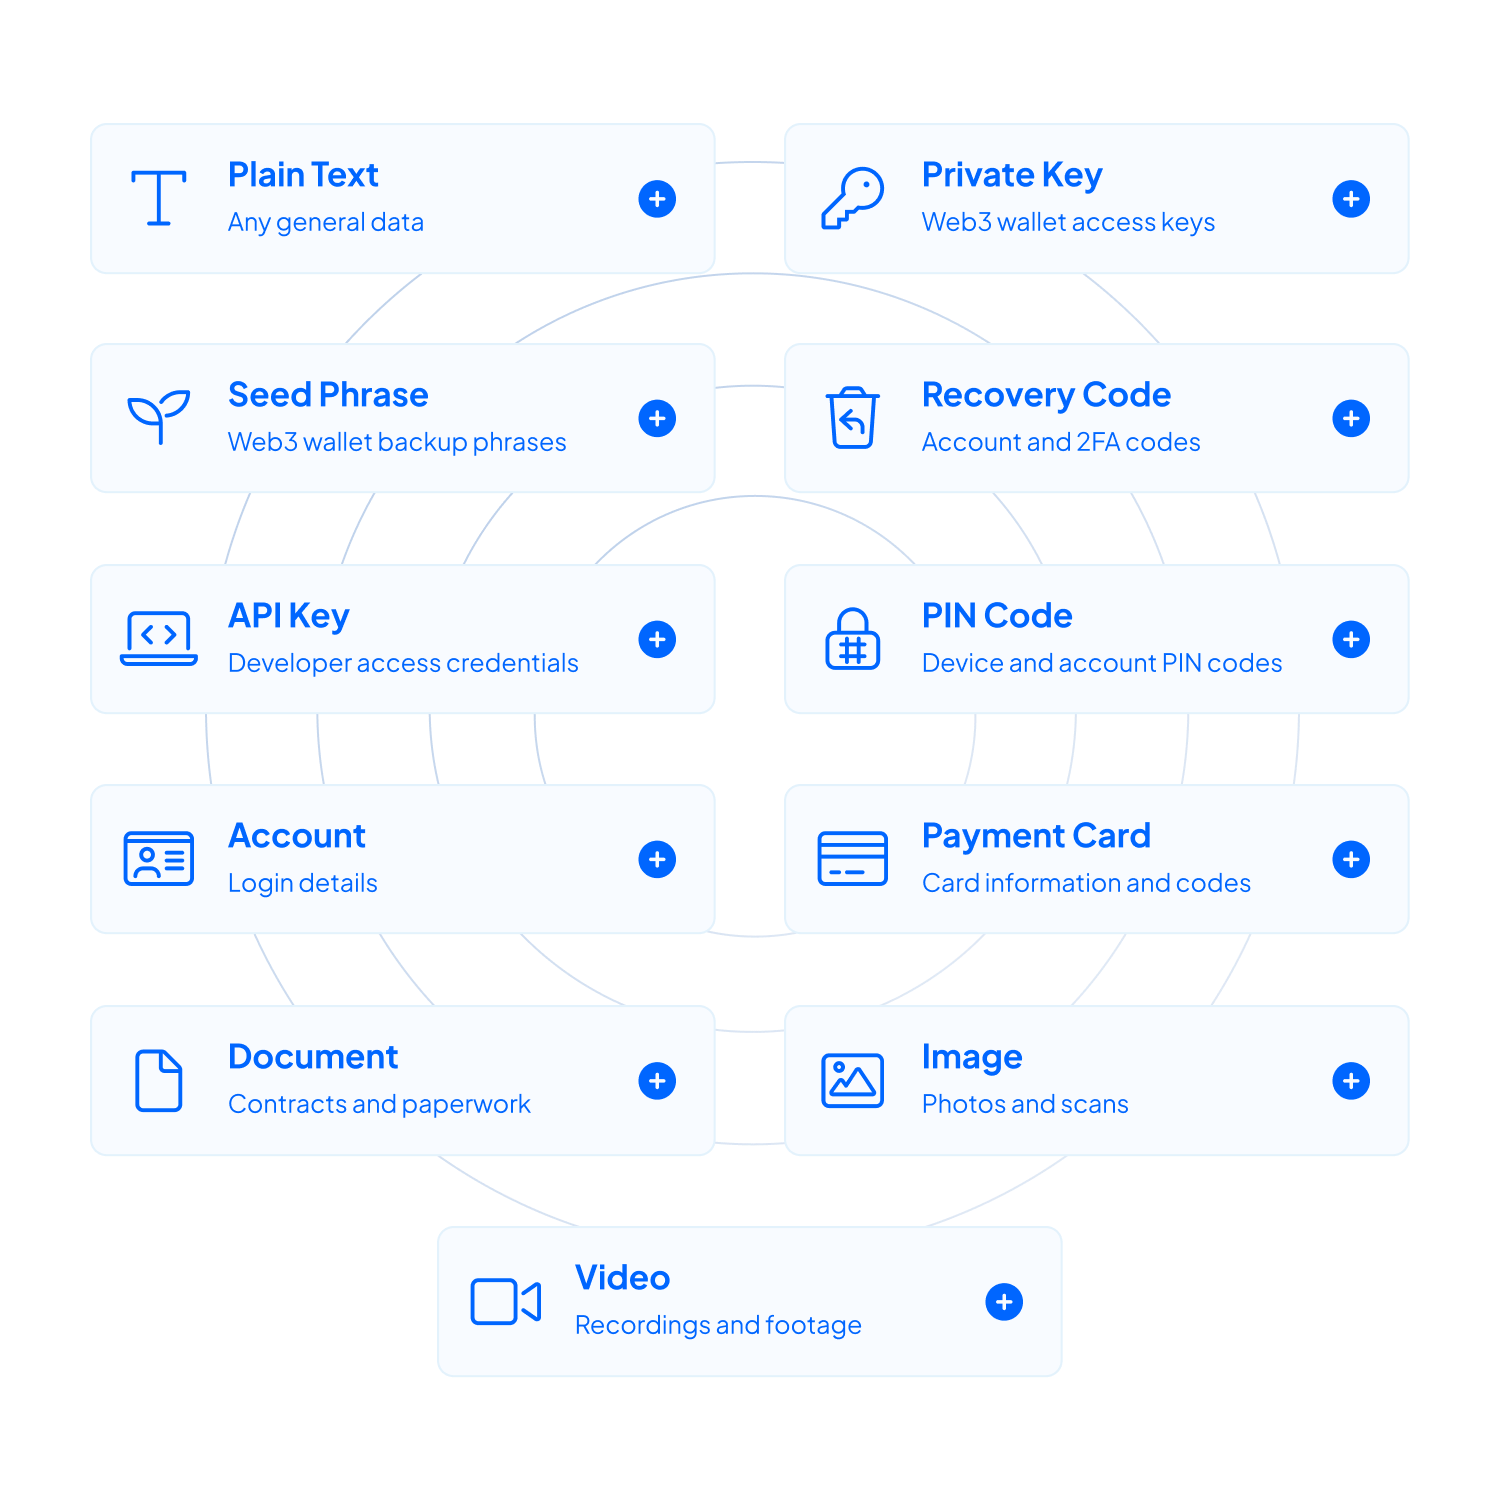
A plan holds the real thing: plain text, private keys, seed phrases, recovery codes, API keys, PIN codes, account logins and payment cards, and documents, images and video as well. Every asset is encrypted in your browser before it leaves the device, then split into shares that are useless on their own.
An authorised member opens the asset inside Inheriti® Business and can use it. What changes is that their access is checked against their team membership at the moment they open it, that you can require other members to approve first, and that every opening is recorded.
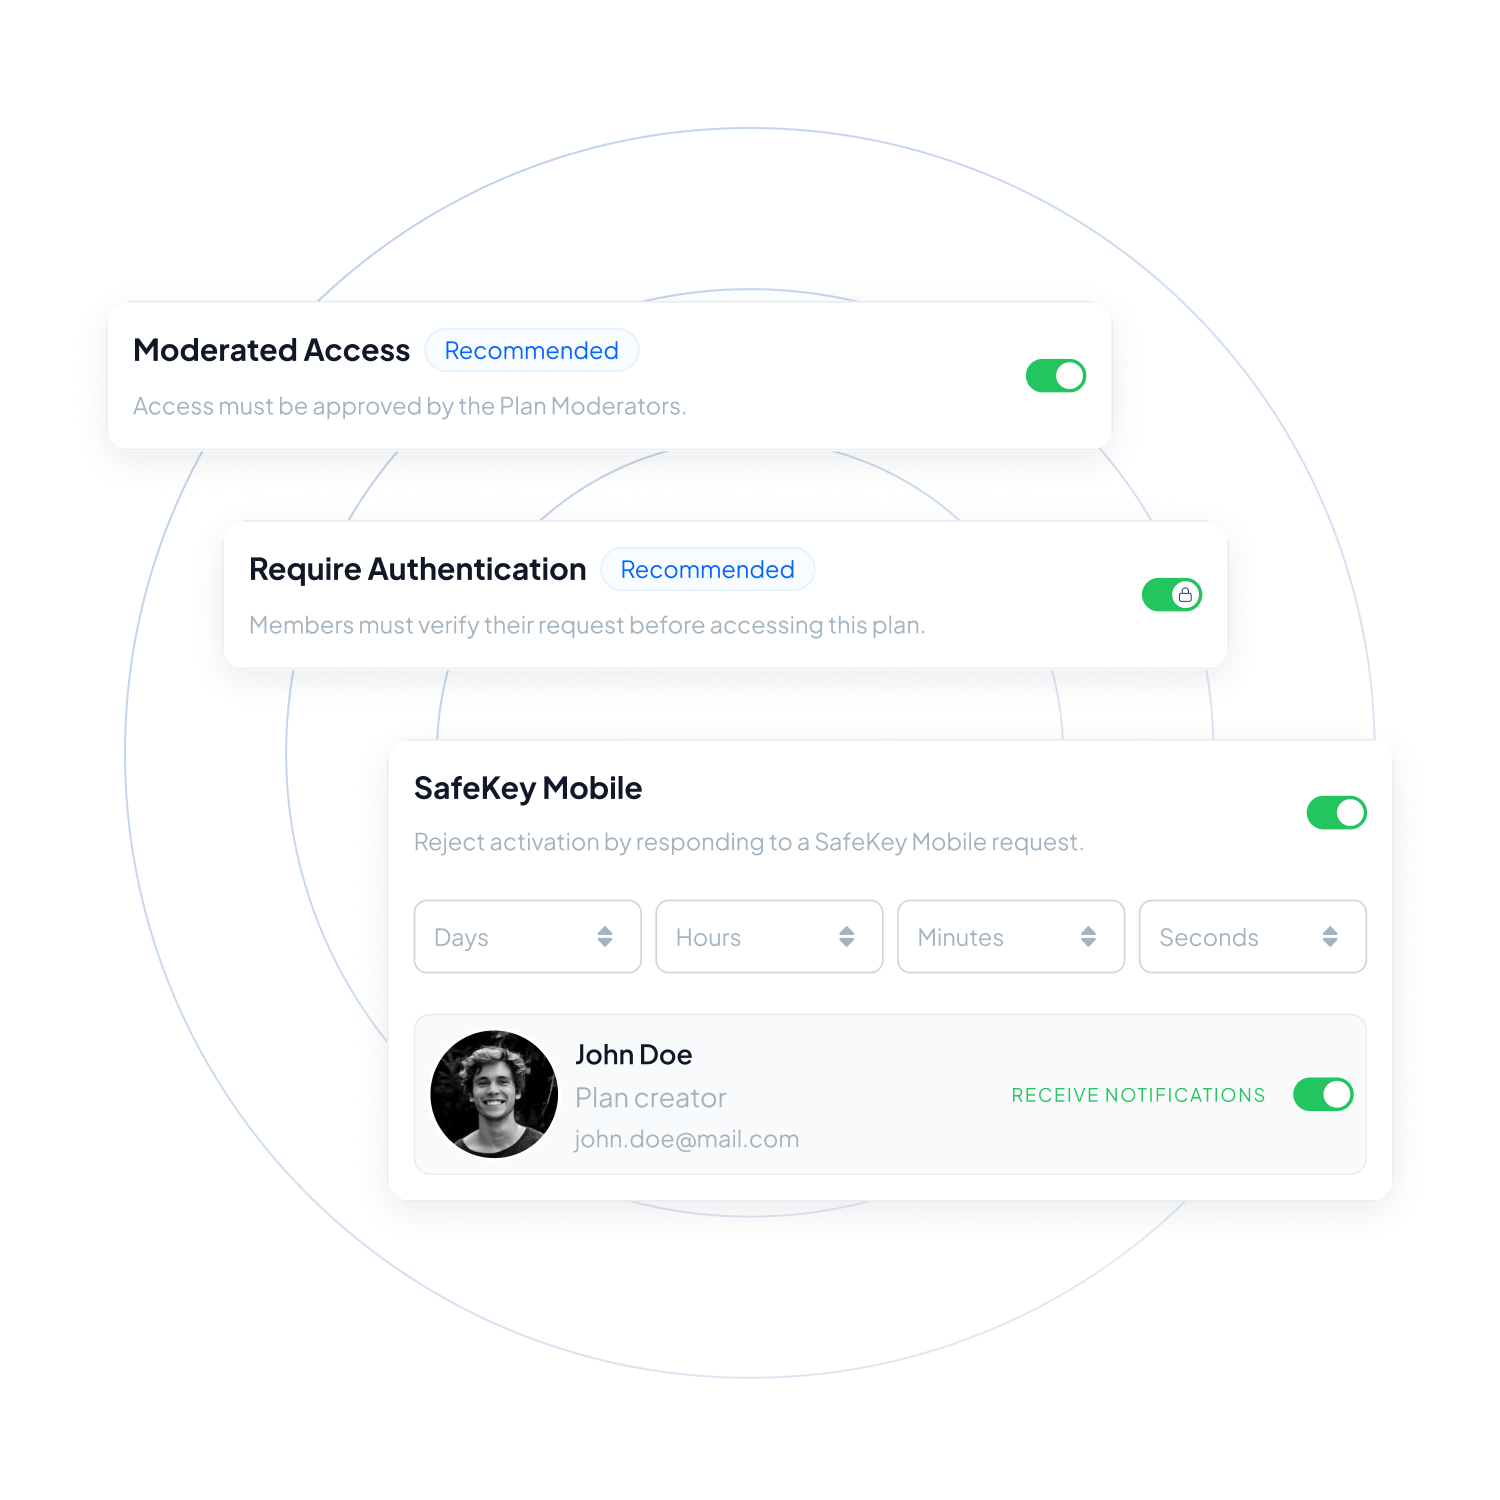
You decide how heavy the gate is on every plan:
The gates compose, and no plan is ever left unguarded: switch authentication off and moderation becomes required. Every request, approval and reveal lands in the audit trail.
The shares are spread over separate layers, and every layer is needed to put a secret back together. A threshold belongs to the approvals, not to the storage.
The SafeTech-run cloud layer that holds the encrypted data shares. Included in every tier, and home to the custodian depot.
Our own chain. Your organisation’s smart contract holds the validator key shares that gate every access.
The managed hardware security module that seals every plan key. It stores nothing and can open nothing on its own.
Connect Dropbox, Google Drive or OneDrive as a paid add-on layer. Each one takes a share of its own, so it becomes part of the reconstruction rather than a spare copy.
Handing the keys to a supplier only moves the risk. If they are breached, you are open.
Your organisation key is derived in your own browser, with Argon2id, from a passphrase only the organisation owner knows. It never reaches our servers: the backend keeps a salt and a non-reversible verifier, nothing that can be turned back into the key. That key wraps every plan key, and our hardware security module then seals the result with a key pair that never leaves the device.
At reveal the module peels off its own layer only, and hands back something still encrypted under a key it has never held. Full access to our database, our storage and our hardware is still not a path to your data.
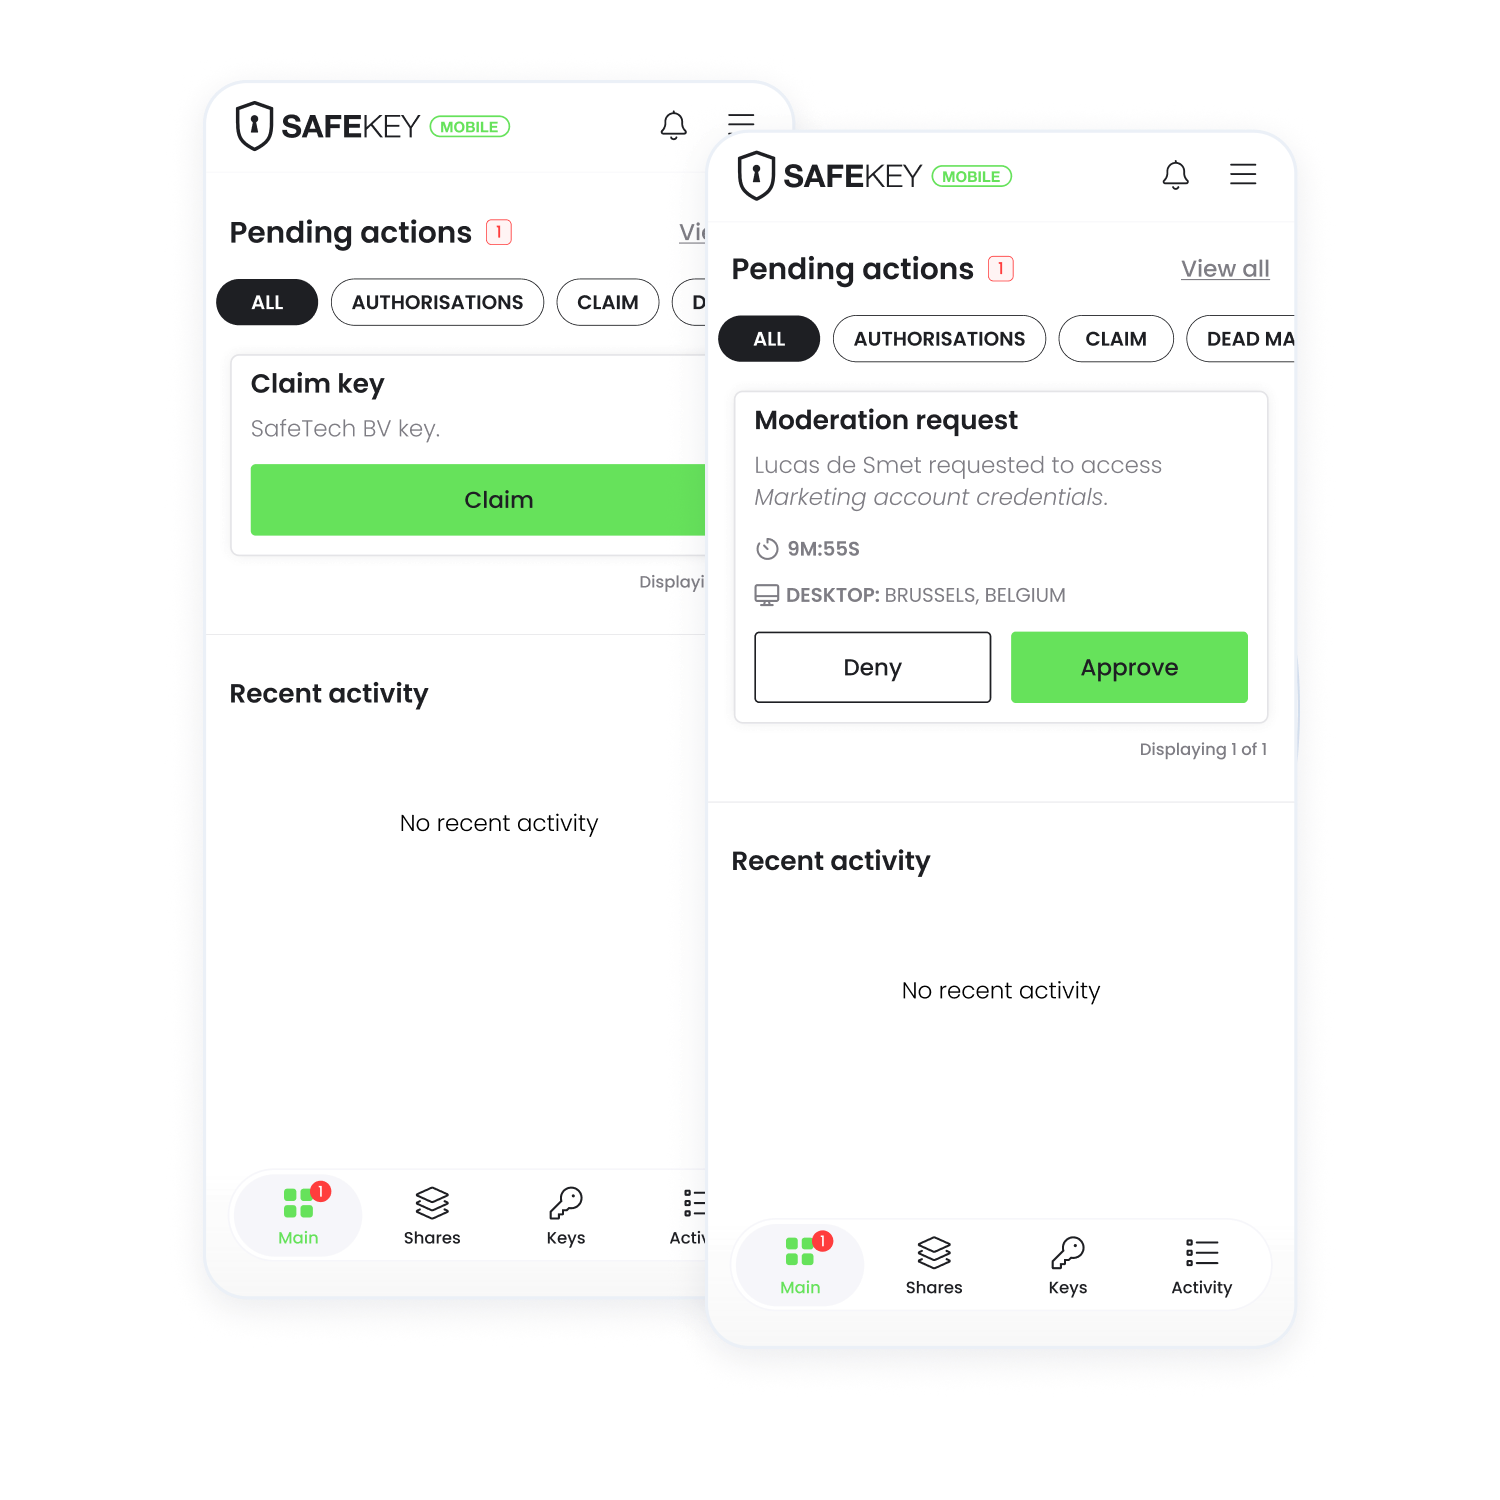
SafeKey Mobile holds each member’s key material and approvals: claiming the organisation key, confirming an access request, responding to a Dead Man Switch. The device’s private key never leaves the phone.
SafeKey Pro keeps key shares offline, in cold storage, for the material you want off any network at all.
Protect company credentials without everything running through one person.
Roll out secret sharing across teams, departments, and offices at scale.
Remove credential bottlenecks and set proper access controls across the org.
Keep financial credentials accessible during handovers, absences, or emergencies.
Keep systems running even when key people aren’t around.
Hand credentials over securely when someone leaves, so nothing gets locked out.
Inheriti® Business brings secret sharing, continuity and provable governance to teams. Set up your organisation in minutes.
Tell us about your organisation and we’ll be in touch about joining the Inheriti® Business pilot in 2026.
 Nederlands
 Français
 Español
 Deutsch